Cellular SASE for connected devices, Zero Trust security delivered by SIM

Built by one of the first global connectivity players to integrate with the three leading SASE vendors - Palo Alto Networks, Zscaler and Fortinet - Transatel Cellular SASE lets enterprises extend their existing SASE and Zero Trust architecture to IoT devices without switching security partners.

Built in partnership with

Fortinet
Palo Alto Networks
Zscaler

More connected devices. More critical assets. More exposure.

Enterprises are now deploying large fleets of connected devices globally, relying on cellular connectivity for mission-critical services. This scale and distribution create security challenges that endpoint tooling was never designed for.

Connected assets increasingly operate:

  • Outside corporate security perimeters
  • Across multiple countries and regulatory domains
  • On multiple network operators and infrastructures
  • Often without human supervision or direct management

The result is fragmented security models, uneven policy enforcement and limited end-to-end visibility - a materially larger attack surface and more operational risk. Security has to move from the endpoint to the connectivity layer, where access, identity and policy can be enforced consistently at scale.

Engineer working on a laptop in a data center
5.1 billion Cellular IoT connections projected by 2030
$4.4 million Average cost of an enterprise data breach
400% increase Increase in IoT and OT malware attacks

Introducing Cellular SASE: Security by the SIM

Traditional model

Today: one guard, at head office

Your stores, vehicles or machines

Headquarter Internet & your apps

Bridged by agents & gateways, not built for constrained IoT

Connectivity and cybersecurity have traditionally been separate layers: mobile networks provide connectivity and device identity, while security controls access to applications, the Internet and enterprise data

IoT is different. Resource-constrained, purpose-built and remotely managed devices often cannot support traditional endpoint security agents

Cellular SASE

A guard at every door

Every device, verified at its own door

Internet & your apps

One architecture, one controlled entry point

Cellular SASE extends SASE principles to cellular and IoT environments, embedding connectivity and security directly into the mobile network, with no need for an on-device agent

Security becomes part of connectivity, unifying cellular access and Zero Trust controls in a single architecture.

1 architecture, 3 partners

Each SASE partner provides the security capabilities and policy enforcement layer

Fortinet Palo Alto Networks Zscaler

FWaaS: Firewall as a Service

Applies firewall security policies from the cloud.

ZTNA: Zero Trust Network Access

Continuously verifies users and devices before allowing application-level access.

CASB: Cloud Access Security Broker

Monitors and secures the use of cloud applications.

SWG: Secure Web Gateway

Filters and controls Internet access. Blocks malicious or inappropriate websites.

DLP: Data Loss Prevention

Detects and prevents sensitive data from leaving the company.

DNS Security

Blocks connections to known malicious domains.

Centralized Management

Manages networking and security policies from a single platform.

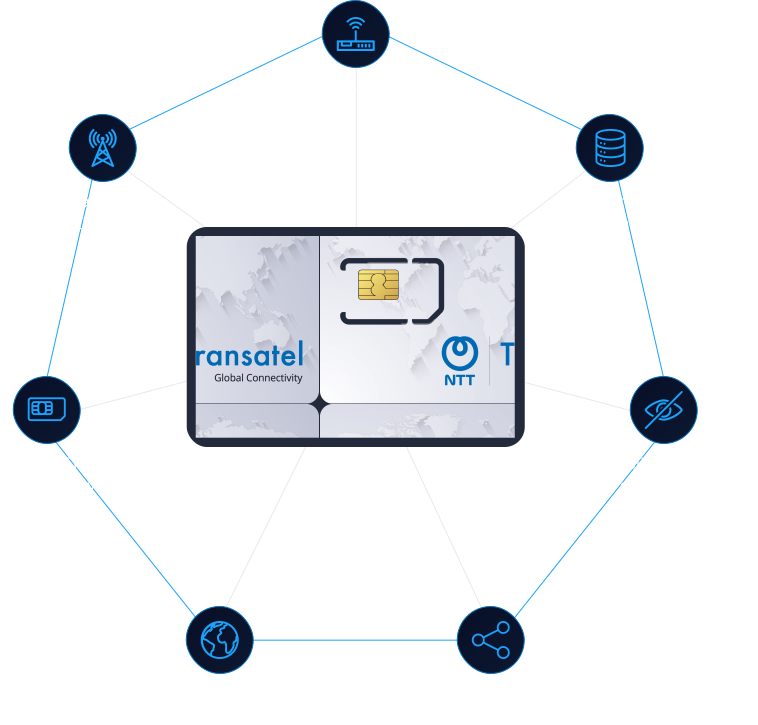
Connectivity layer

provided by Transatel on which Cellular SASE operates.

Transatel connectivity layer: private cellular connectivity, segmented environments, non-publicly addressable connectivity, multi-operator independence, global deployment capabilities, existing SIM compatibility and standard cellular connectivity methods
NTT managed services: architecture design, end-to-end solution integration, deployment, global managed services and operational support

Managed Services

NTT brings complete architecture into the enterprise operating environment.

Direct business outcomes

with Transatel’s Cellular SASE

Protect critical data

Reduce the risk of unauthorized access, malicious traffic and data leakage.

Protect the applications and data accessed by connected devices.

Accelerate deployment

Extend enterprise security to constrained IoT devices without requiring endpoint security agents or hardware redesign.
Reduce security integration effort and accelerate time-to-market for connected projects.

Enforce global policies

Apply a consistent security model across devices, sites, countries, operators.

One policy framework for a globally distributed IoT estate.

Simplify operations

Converge connectivity and security into a common architecture.

Reduce fragmented technologies, policies and operational processes across network and security teams.

Key use-cases

leveraging Transatel’s Cellular SASE

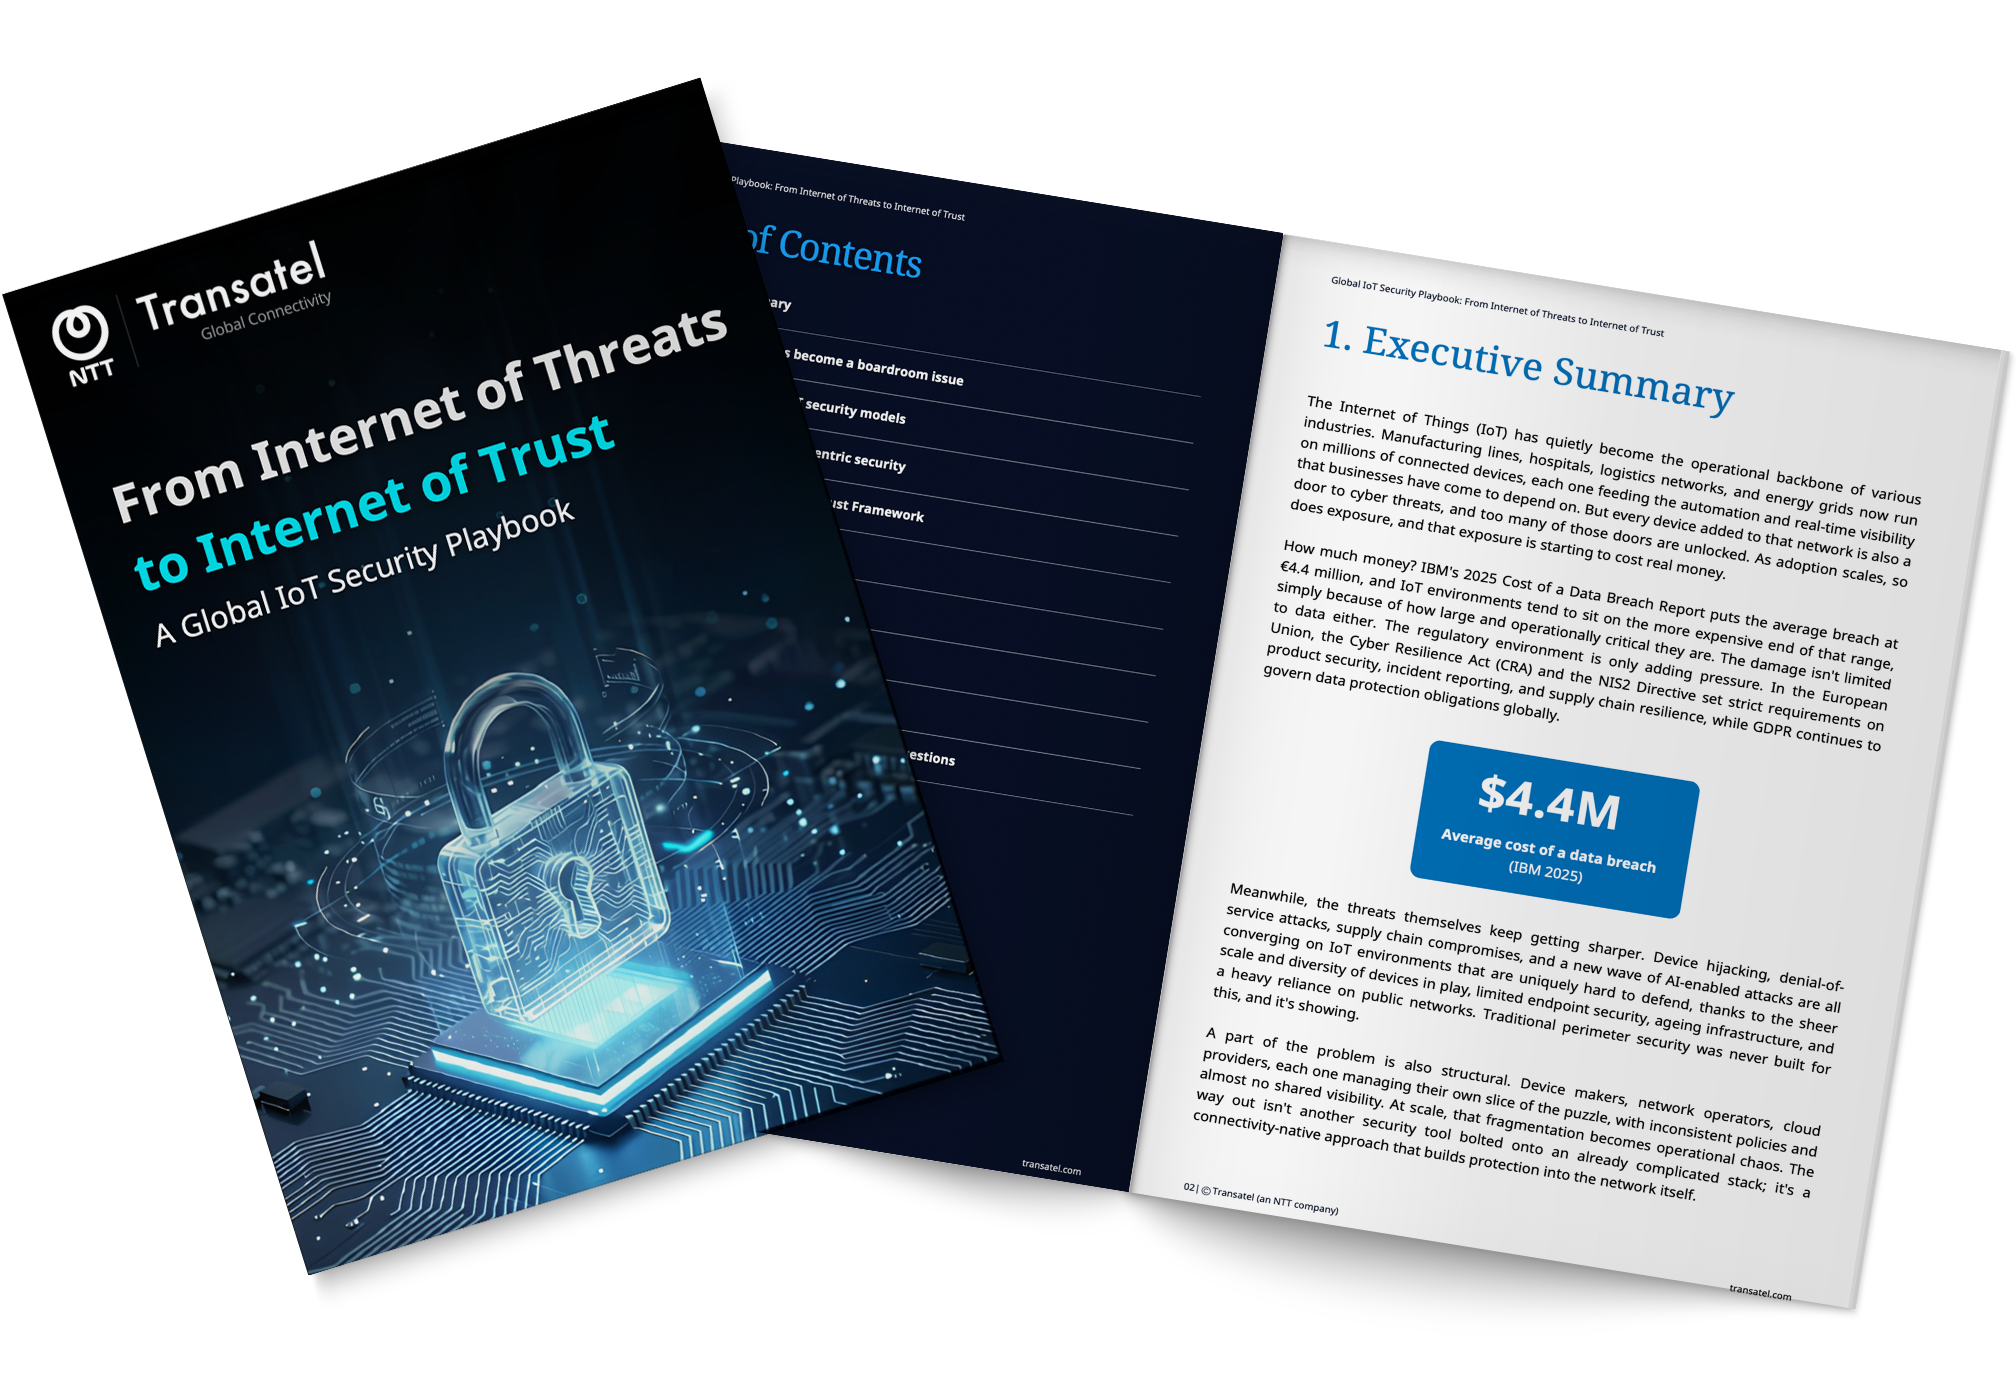
Global IoT Security Playbook: From Internet of Threats to Internet of Trust

Global IoT Security Playbook: From Internet of Threats to Internet of Trust

Discover Transatel’s PRC Trust Framework and network-native security to securely scale and confidently manage global IoT deployments worldwide.

Download

We securely connect

Airbus
SNCF
Worldline
Infrabel
SITA
Air France KLM
Eiffage
Fonroche Lighting
Mitsubishi Electric
Kubota

Book a FREE meeting with our global IoT experts

Connect IoT devices

Speak with our experts to assess your needs and accelerate your connectivity roadmap

  • 25+ years of excellence in telecom
  • Connectivity partner for 650+ enterprises
  • Seamless coverage in 200+ countries & territories
  • 2G, 3G, 4G, 5G and LTE-M connectivity
  • Available in 1FF, 2FF, 3FF, 4FF, MFF2 & eUICC SIM formats
  • Never pay for inactive SIMs again

Frequently asked questions

Cellular SASE extends SASE principles to cellular and IoT environments, embedding connectivity and security directly into the mobile network, with no need for an on-device agent.

Traditional models rely on agents and gateways that resource-constrained IoT devices often cannot support. Cellular SASE enforces access, identity and policy at the connectivity layer instead, with a guard at every door rather than one guard at head office.

Through the Transatel SIM and its global connectivity layer, integrated with the security capabilities of Palo Alto Networks, Zscaler and Fortinet.

Enterprises can extend their existing SASE and Zero Trust architecture to their IoT devices without switching security partners.

It is built for connected devices such as stores’ PoS terminals, vehicles or machines, which rely on cellular connectivity and often cannot run traditional endpoint security agents.

NTT managed services cover architecture design, end-to-end solution integration, deployment, global managed services and operational support.

Your message has been send to us.

Close